Respond quickly instead of searching for hours
Real-time detection with clear alerts for time-critical actions.
The Attack Defense Sensor (ADS) continuously monitors your network traffic, detects suspicious activities in real time, and prioritizes critical alerts. This allows you to maintain visibility, reduce false alarms, and respond faster and more precisely without overloading your teams.
Separate relevant signals from noise
Visibility is the foundation of effective cyber defense. In heterogeneous environments with multiple locations, remote access, and cloud services, the number of suspicious events increases – along with the pressure on your teams to separate relevant signals from noise. You are responsible for availability, compliance, and effective incident response – with limited resources and without rewarding false alarms.


The ADS is a network-based sensor that analyzes traffic patterns, detects attack indicators, and triggers real-time alerts when suspicious activity is detected. Its rule set covers more than 40 categories (including malware command and control, credential phishing, DDoS/botnets, network anomalies, exploits, vulnerabilities, and exploit kits) and is updated daily. The goal is to reliably identify critical activities. The result: fewer blind spots, less noise, and faster, well-informed responses.
Real-time detection with clear alerts for time-critical actions.
Effectively complements existing firewalls/IDS/IPS without replacing their operation.
Targeted detection of CO2, botnets, phishing consequences, and exploits before damage occurs.
Monthly reports with alerts by category and an overview of IT compliance violations – including src_ip and dest_ip for audit-proof tracking.
Reduce outages, data loss, and consequential costs through early detection.
Security Dashboard with total filtered events, critical alerts, and their geolocation – available at any time.
What you can see at a glance
From event overload to prioritized actions in seconds
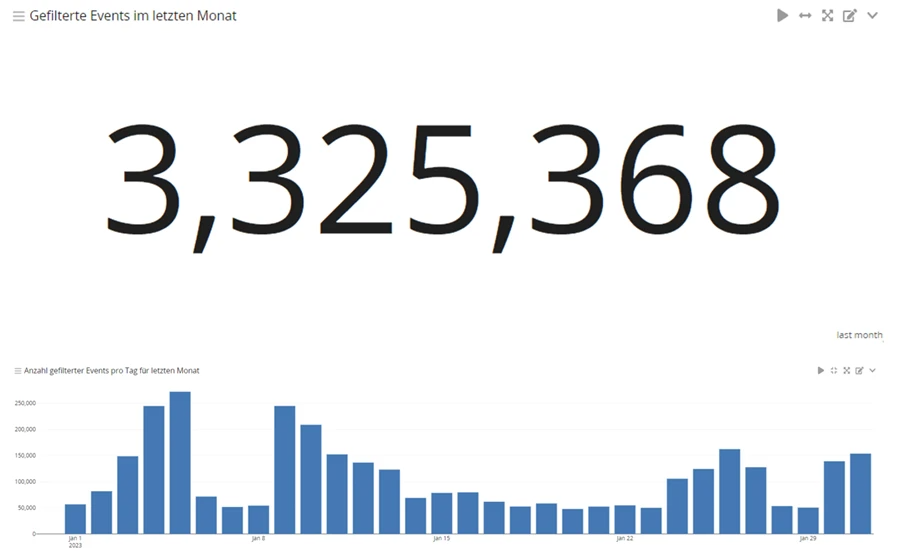
In the Security Dashboard, you can see the total number of filtered events, prioritized critical alerts, and their geographical origin at a glance. This allows you to immediately identify where action is required, focus your resources, and accelerate incident response and management reporting.
Monthly analysis, permanently available in the dashboard
Customer reports are provided to you on a monthly basis. With the dashboard, you still have the option to access and review the content at any time.
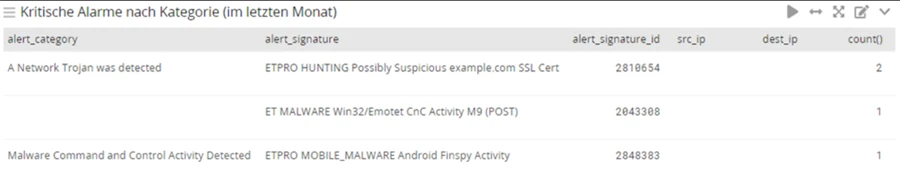
Critical alerts by category
We show you which critical alerts occurred, in which category, and with which src_ip and dest_ip.
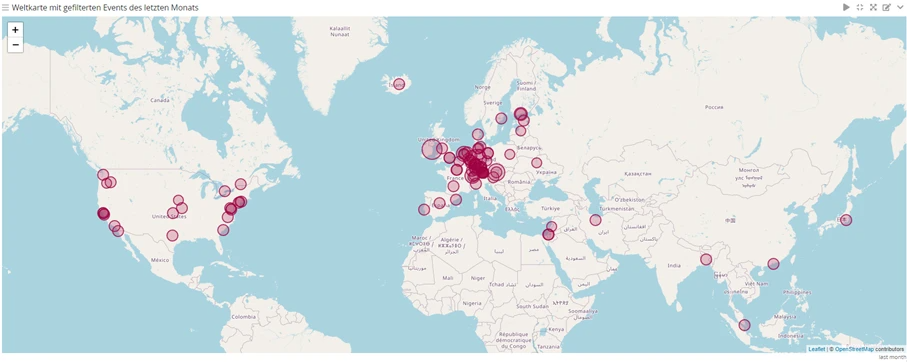
World map
With the world map, you can see at a glance where the events filtered by us have occurred.
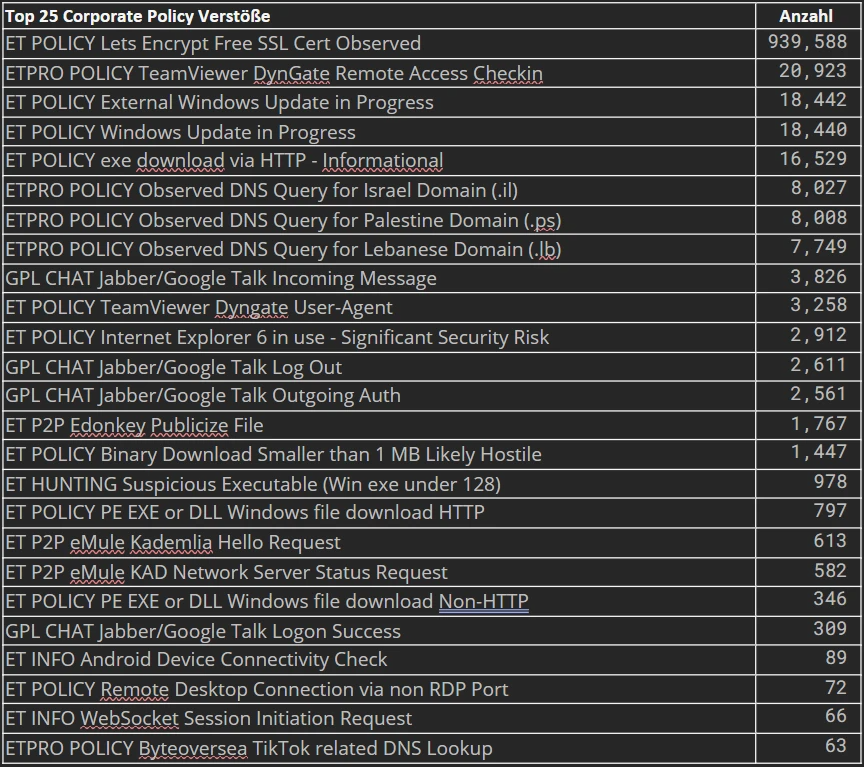
IT compliance violations
The configured table provides you with an overview of compliance violations within your organization. The report also includes the src_ip and dest_ip, allowing you to trace where the compliance violation occurred.

Experience, clarity, and reliability
We speak the language of IT management, network, and security teams – from requirements to implementation. We help you interpret signals, prioritize risks, and define meaningful response paths without leaving you alone with unnecessary detail and noise. Daily updated rule sets, structured reports, and a dashboard that supports decision-making create operational security and reliability. The solution starts with clearly defined use cases and can be expanded flexibly to additional locations and segments based on your needs.

Are you interested in our Attack Defense Sensor? Feel free to contact us via the contact form.